OperateGovernance
Contextual Access
have broad access to tools, but enterprises need fine-grained control. Arcade’s contextual access lets you govern visibility and behavior at every stage of execution — who can see a tool, what inputs are allowed, and what comes back.
You connect your own access-control, compliance, or transformation logic to the Arcade Engine. Your rules run inline during with no changes to your tools or required.
What you can do
- Control visibility — Decide which tools each can see based on role, team, entitlement, or any signal from your IDP
- Validate requests — Enforce policies before execution (e.g., block certain domains, require org-scoped inputs)
- Transform payloads — Enrich inputs, inject secrets, redact PII from outputs, or filter content
- Audit every interaction — Route all calls through your security and logging infrastructure
How it works
Contextual access is powered by Logic Extensions, a framework that allows you to hook in and add logic directly to Arcade’s execution flow. Arcade calls your server at three predefined hook points in the lifecycle:
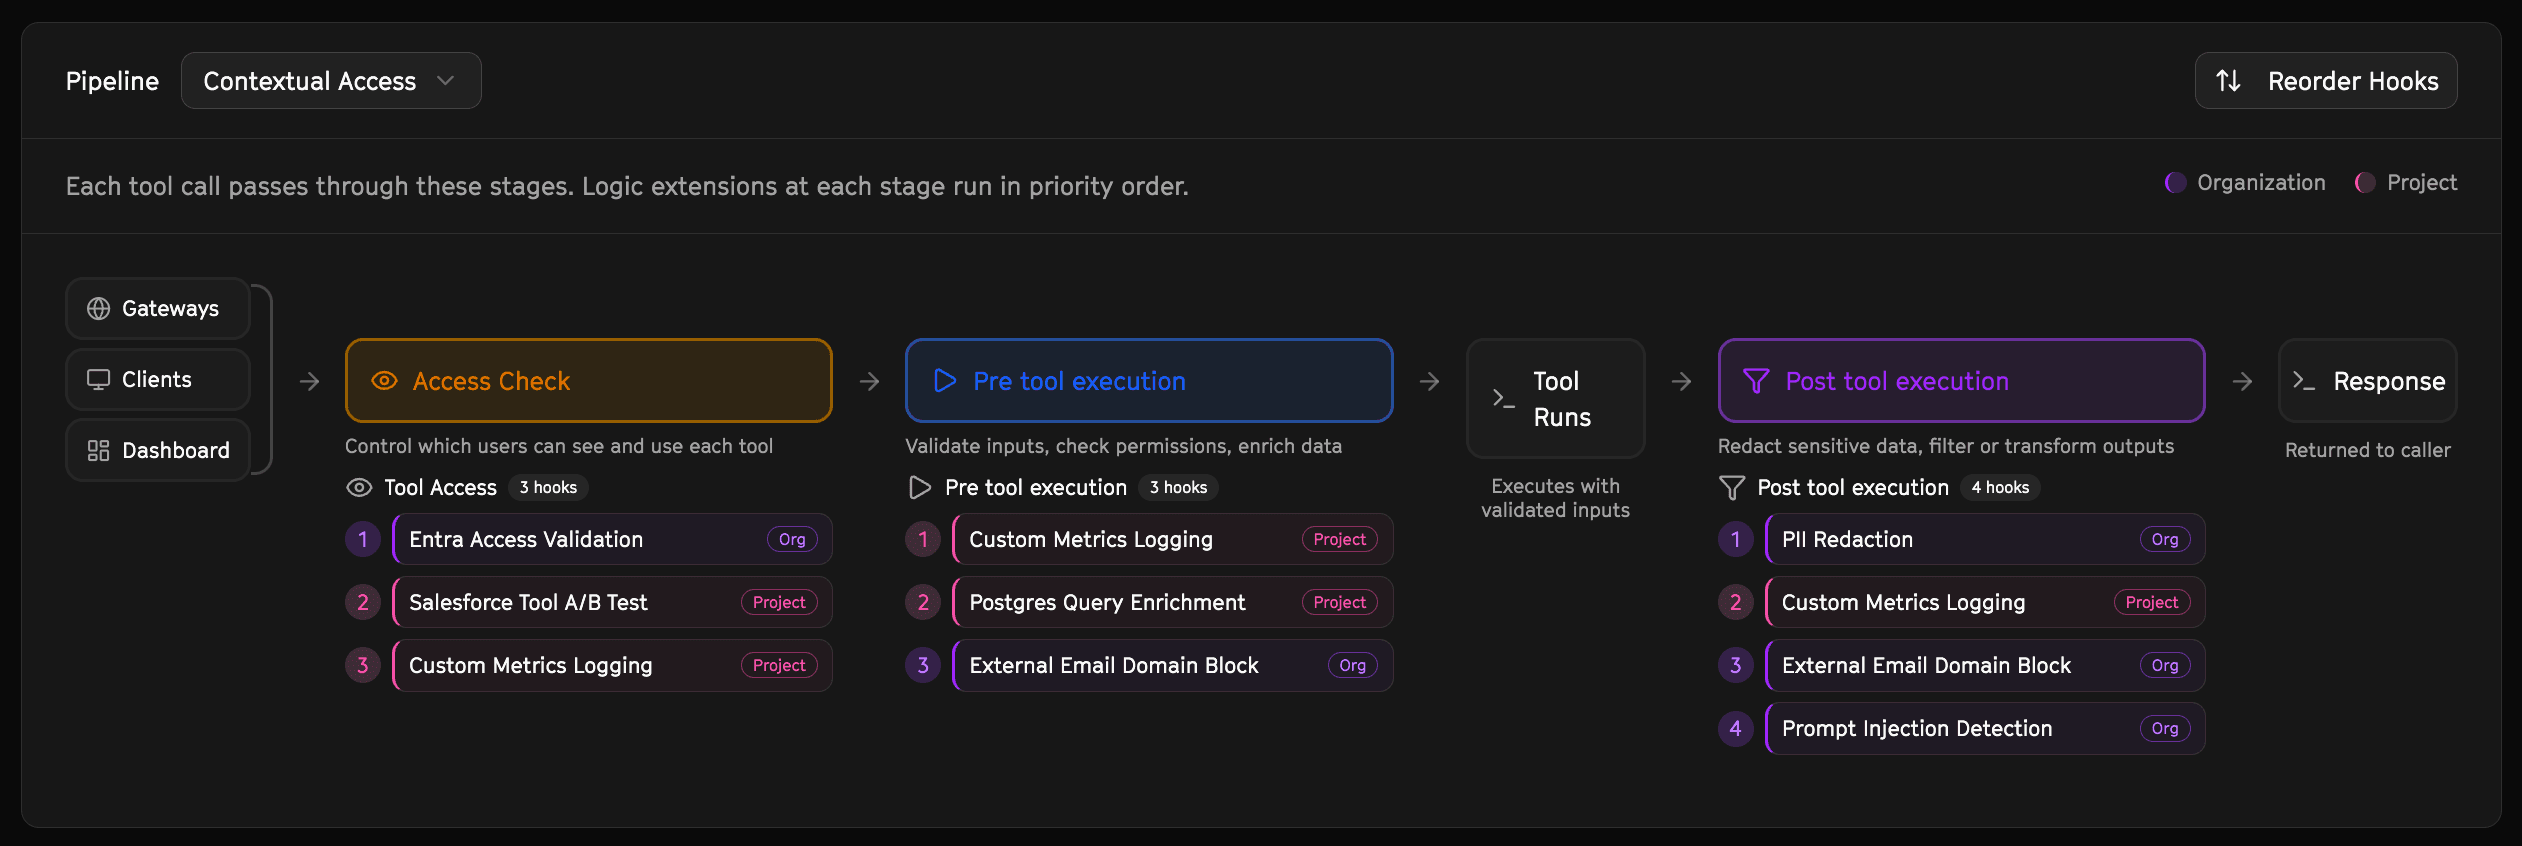
| Hook point | When it runs | What it can do |
|---|---|---|
| Access Hook | When listing tools for a user | Allow or deny tools the user can see |
| Pre-Execution Hook | Before each tool execution | Allow, deny, or modify inputs |
| Post-Execution Hook | After tool execution | Allow, deny, or modify the result (output and content blocks) |
You only implement the hooks you need. Configure everything through the Dashboard.
Get started
Edit on GitHub
Last updated on